


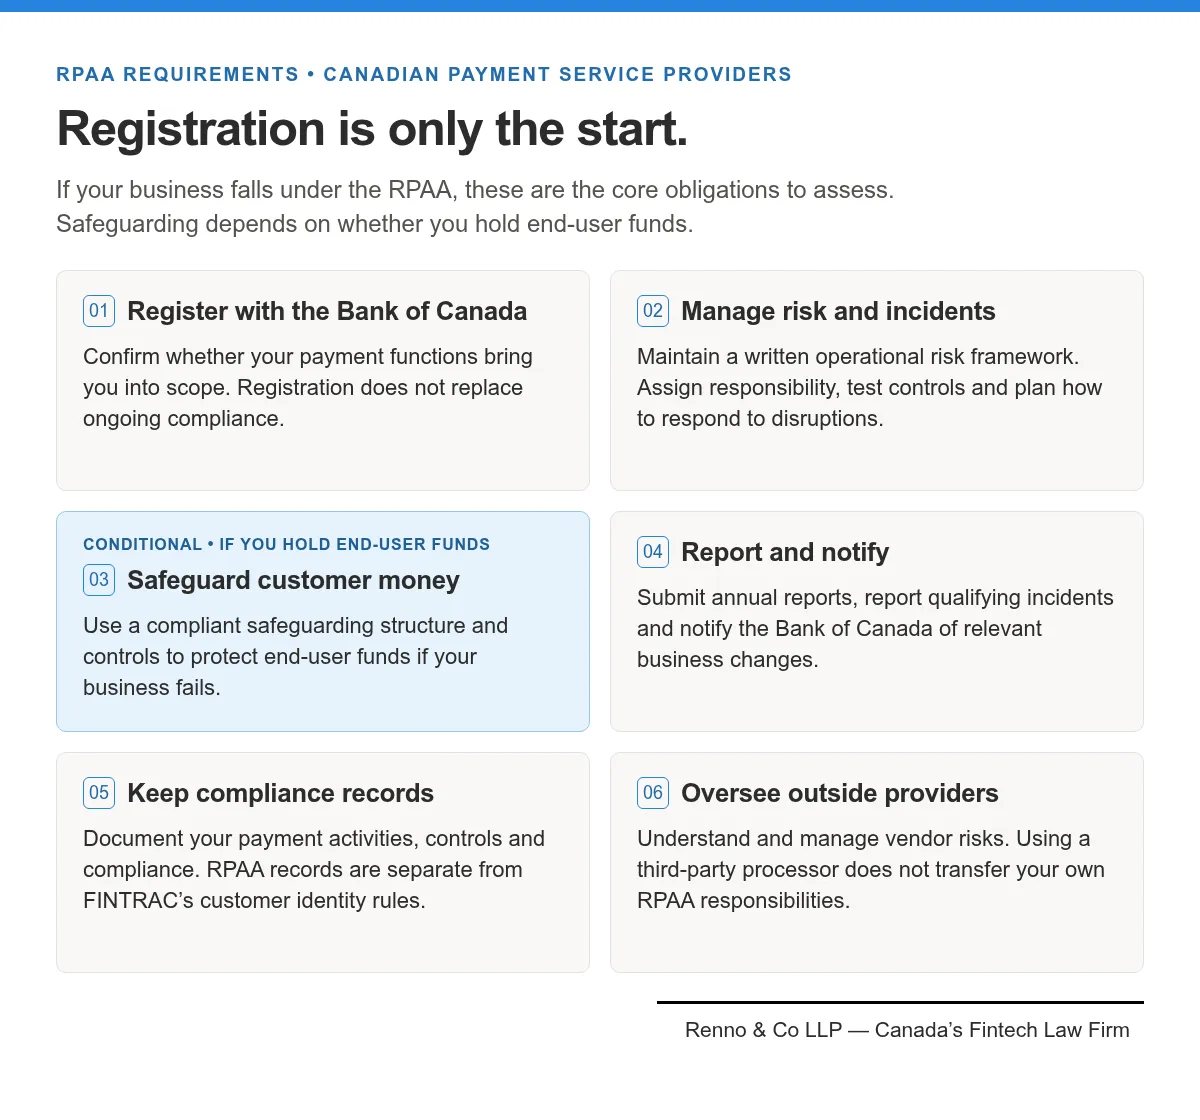
The Retail Payment Activities Act ("RPAA") requires payment service providers ("PSPs") with a connection to Canada to register with the Bank of Canada and then meet a set of ongoing requirements. The core RPAA requirements are registration, an operational risk management framework, safeguarding of any end-user funds you hold at rest, incident reporting, annual reporting, recordkeeping, and oversight of your third-party providers. Registering is only the start. Most of the real work is staying compliant afterward.
Here is the nuance that trips people up: not every requirement applies to every PSP. Registration and operational-risk obligations can apply even if you never touch customer money. But safeguarding obligations only apply when you actually hold end-user funds. Below, you will learn what each requirement means, who it applies to, and where PSPs most often get caught off guard. Along the way, you will follow a software company we will call Assembly, which realized it might be a payment service provider without ever setting out to become one.
What is the Retail Payment Activities Act (RPAA)?
The RPAA is the federal law that governs retail payments in Canada. The Bank of Canada administers it, and it focuses on two things: operational risk and the safeguarding of customer funds. The goal is to protect end-users by making sure PSPs run reliably, handle problems properly, and keep customer funds safe if the business fails. It is a registration regime, not a licensing regime.
That distinction matters. There is no "RPAA licence." What you actually get is Bank of Canada registration as a PSP. Being registered also does not mean you are compliant. Registration gets your name on the register; the operational requirements below are separate obligations you have to meet and keep meeting.
The framework is live today, so this is a current obligation, not something to prepare for later. PSPs that submitted their application before September 8, 2025 were allowed to begin providing payment services even before their registration was finalized. You can confirm where a company stands using the Bank of Canada's PSP registry and its list of applicants.
Who must comply with the RPAA?
You must register and comply with the RPAA if you perform a payment function and have a connection to Canada. A connection means Canadian incorporation, people or a place of business in Canada, or serving Canadian clients. Unlike the money services business rules, the RPAA has no reverse-solicitation exemption. Serving Canadians can pull you in even if you do not market to them. Pay-in and payout products are the usual candidates.
In plain terms, the RPAA tends to apply when you help someone send electronic funds to a third party, or help someone receive electronic funds from a third party. You can be captured even if you never hold the money yourself. Being registered as a money services business does not automatically mean you need RPAA registration either. It depends on the payment functions you actually perform. For the full who-must-register test, see our RPAA registration guide.
This is where Assembly comes in. Assembly is an established Canadian software platform that moves a large volume of payments each year through an outside payment processor. For years it assumed it was "just software." When it reviewed the rules, it realized those payment flows might be a regulated payment function, which would make it a PSP. Whether a platform like Assembly is truly in scope depends on the specific functions it performs, so this is a question to work through carefully rather than assume. Assembly also discovered it had missed the early registration window, which is a common "we did not realize we were in scope" moment rather than a sign of bad faith.
What are the main RPAA requirements for PSPs?
Once you are in scope, the RPAA gives you a set of core requirements. Some apply to every registered PSP, and one of them, safeguarding, only applies if you hold end-user funds. Here is the full picture in one place before we go deeper on the big ones.
RPAA requirements at a glance
| RPAA requirement | What it involves | When it applies |
|---|---|---|
| Registration | Register as a PSP with the Bank of Canada before you provide payment services | Every PSP with a Canadian connection |
| Operational risk management framework | A written framework to manage operational risk, resilience, and incidents | Every registered PSP |
| Safeguarding end-user funds | Hold funds in a protected, trust-style account with a daily ledger and reconciliation | Only PSPs that hold end-user funds at rest |
| Incident reporting | Report significant incidents to the Bank of Canada and affected parties | Every registered PSP |
| Annual reporting | File a report each year on your payment activities | Every registered PSP |
| Recordkeeping | Keep records that show you meet your obligations | Every registered PSP |
| Third-party oversight | Manage the risks of vendors and outsourced providers | PSPs that rely on third parties (most) |
| Governance and accountability | Clear responsibility for controls, testing, and remediation | Every registered PSP |
What are the operational risk management and incident response requirements?
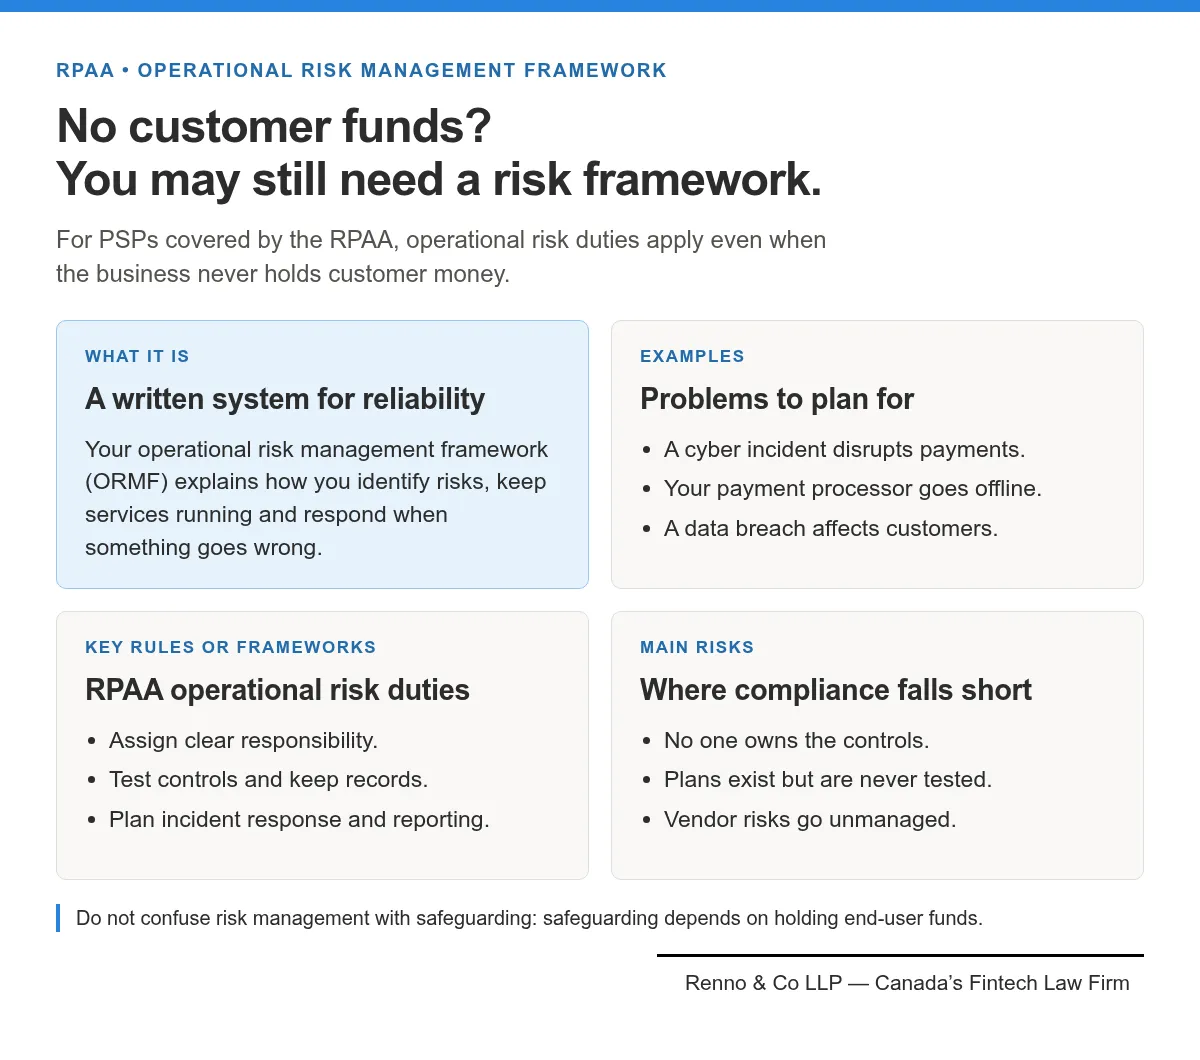
Every registered PSP needs an operational risk management framework ("ORMF"). This is a written framework that explains how you identify operational risks, keep your service running, protect against things like fraud and cyber incidents, and respond when something breaks. It also covers who is accountable, how you test your controls, and how you manage the vendors you depend on. This obligation applies whether or not you hold customer funds.
Think of the ORMF as turning good intentions into a system. The Bank of Canada does not want ad hoc firefighting. It wants a real program: clear accountability for controls, regular testing, documentation that proves the program is actually running, and a plan for detecting and reporting incidents that affect customer funds or data. Because most PSPs lean heavily on outside providers, managing that supplier and outsourcing risk is part of the framework too.
If you want a deeper walkthrough of this piece, read our guide on whether PSPs need a risk management framework. For Assembly, this is the requirement it underestimated most. It could register, but it still had to build a working ORMF before it could honestly say it was compliant.
When must PSPs safeguard end-user funds?
Safeguarding only applies when you hold end-user funds at rest, meaning customer money that sits with you and is available for later use. If funds only ever pass straight through, or you never hold customer money at all, the specific safeguarding rules may not apply to you. So "all PSPs must safeguard customer funds" is simply not true. It depends on your model.
When safeguarding does apply, it is more than opening a second bank account. The common route is a trust structure: you hold the funds in a safeguarding account at a qualified financial institution, set it up so the money is legally treated as end-user property, and run daily controls so the records stay accurate. That usually means a daily ledger of who owns what, daily reconciliation, and a "sweep" that moves customer money out of busy operating accounts into the safeguarding setup on a clear schedule.
The point is bankruptcy protection: if your company fails, customers should be able to get their money back instead of standing in line with other creditors. A label like "FBO" or "client money account" is not enough on its own if the legal structure and controls are missing. For the full mechanics, see our guide on safeguarding end-user funds.
What must PSPs report to the Bank of Canada?
Registered PSPs have ongoing reporting duties. You file an annual report each year covering your payment activities, and you report significant incidents, such as a fund loss or data breach, to the Bank of Canada and to the parties affected. You also notify the Bank of Canada about certain changes to your business. These duties are continuous, not one-time.
Not every change is treated the same way, so do not assume you need approval before every operational tweak. Changes generally fall into three buckets: a significant change notice, which can require advance notice; a lighter non-significant change notice; and an update to your registration information. A change of control, where more than one-third of ownership changes hands, is the heaviest case. It triggers a re-registration application, and you must be re-registered before the deal closes. In practice, the Bank of Canada has been prioritizing re-registrations, often turning them around in roughly two weeks.
For how to handle a reportable incident, see our guide on incident response under the RPAA.
What recordkeeping and third-party oversight requirements apply?
Registered PSPs have to keep records that show they are actually meeting their obligations, and they have to manage the risk of the vendors they rely on. Recordkeeping here is about documenting your compliance, your controls, and your payment activities. It is not the same as FINTRAC's customer identity rules, so do not confuse RPAA recordkeeping with AML know-your-customer obligations.
Third-party oversight matters because most PSPs do not run every part of the payment chain themselves. Using an outside processor does not hand your RPAA obligations to that processor. You still have to understand what your providers do, manage the risks they create, and be able to show the Bank of Canada that you have that oversight in place. For more on this, see our guide on third-party service providers under the RPAA.
This is a direct lesson from Assembly's situation. It moved money through a third-party processor, but that arrangement did not make the processor responsible for Assembly's RPAA compliance. The obligations followed Assembly's own payment functions.
How do RPAA requirements differ from FINTRAC's AML requirements?
The RPAA and FINTRAC's anti-money-laundering ("AML") rules are two different regimes with different purposes. A money services business ("MSB") registers with FINTRAC under Canada's AML law to help detect and prevent money laundering and terrorist financing. A PSP registers with the Bank of Canada under the RPAA to protect end-users through operational reliability and fund safeguarding. Many fintechs need both, but one does not automatically create the other.
RPAA and FINTRAC obligations compared
| Comparison factor | FINTRAC / MSB registration | Bank of Canada / RPAA (PSP) |
|---|---|---|
| Main purpose | Detect and prevent money laundering and terrorist financing | Protect end-users through operational reliability and fund safeguarding |
| Regulator | FINTRAC | Bank of Canada |
| Core obligations | AML program, know-your-customer checks, transaction monitoring and reporting | Risk management framework, safeguarding, incident and annual reporting |
Because the two regimes overlap for so many clients, a few points are worth clearing up. Being an MSB does not automatically make you a PSP. Your FINTRAC MSB registration, and separate items like a Québec MSB licence, are their own regimes, not core RPAA obligations. If you do need both MSB and RPAA registration, Renno offers a combined MSB + RPAA registration package that also includes preparing the AML policy you need for MSB registration and the operational risk management framework you need under the RPAA, so the two workstreams move together instead of tripping over each other.
What about banking and Canadian presence?
Getting registered is only half the battle. Before you can go live, you usually need banking and payment rails in place, and that is often the hardest part of the whole process. Many banks and payment providers treat payments businesses as high-risk and are slow or unwilling to onboard them, so plan for it early.
Two things make onboarding easier, and they also come up in your regulatory filings. First, account providers generally want to see a real Canadian operating presence, backed by proof of address, not just a PO box or virtual office. Second, they want a credible AML compliance function behind the business. On top of that, FINTRAC often expects a genuine Canadian physical presence tied to real business or compliance activity. If you are weighing how to set this up, book a call and we can walk through your structure. You can also learn how we help clients get banked on our account opening page.
Frequently asked questions
Do PSPs need to safeguard funds if they never hold customer money at rest?
No. The safeguarding rules apply to PSPs that hold end-user funds at rest. If you never hold customer money, you can still have registration and operational-risk obligations, but the specific safeguarding requirements may not apply.
Does using a third-party payment processor remove your RPAA obligations?
No. Your obligations follow the payment functions you perform. Outsourcing part of the chain does not transfer your RPAA responsibilities to the processor, and you still have to oversee that provider.
Do PSPs need a separate RPAA compliance officer?
Not as a universal rule. The RPAA is focused on governance and accountability, meaning someone must clearly own your controls, testing, and remediation. That is different from saying every PSP must hire or outsource a dedicated compliance-officer role.
Can a PSP be registered with the Bank of Canada but still be non-compliant?
Yes. Registration and ongoing operational compliance are separate. A PSP can be registered and still fall short on its risk framework, safeguarding, or reporting.
What happens if a PSP fails to meet RPAA requirements?
The Bank of Canada supervises PSPs and can take enforcement steps. For an overview of the consequences, see our guide on RPAA penalties and enforcement.
Not sure which RPAA requirements apply to you?
If you think your business might be a PSP, the most valuable first step is figuring out which of these requirements actually apply to your model, and which do not. That is exactly the gap Assembly faced. Our fintech team can map your payment functions to the RPAA, confirm whether you need to register, and scope the framework, safeguarding, and reporting work. Book a call with our team, or fill out our form and we will get in touch. You can also learn more about how we help on our RPAA registration services page.
This content is for informational purposes only and does not constitute legal advice.
Ready to get started?
Talk To UsBook a Free Consultation
Speak with our fintech legal advisor
about your registration


